Malware & Ransomware
Zero-Day Malware: Meaning, Definition and Real-World Impact
Zero-day malware exploits unknown software flaws before vendors can patch them, leaving traditional signature detection entirely blind to the threat until it executes.
Zero-day malware exploits unknown software flaws before vendors can patch them, leaving traditional signature detection entirely blind to the threat until it executes.
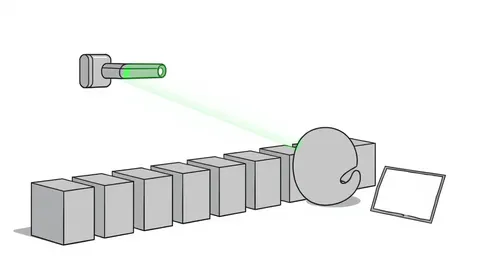
Signature based detection in cyber security identifies known threats with high precision but fails completely against novel code that lacks a recorded fingerprint.
Reconnaissance occurs silently on your internal networks long before any external perimeter breach, rendering traditional perimeter alerts useless against modern adversaries.
Whaling succeeds not through technical brilliance, but by exploiting the natural deference organisations pay to authority figures and established communication patterns.
The Unified Kill Chain exposes the hidden gap between initial access and lateral movement, revealing where small teams waste resources on perimeter alerts.
Small teams face the same attack surface as giants, yet can secure devices through automated policies rather than hiring dedicated security staff.
DDoS protection relies on separating legitimate users from attack traffic by analysing behavioural patterns before data reaches your servers.
DCSync attacks often succeed because administrators grant excessive replication rights to service accounts that should only hold limited permissions.
Breach and attack simulation automates controlled cyber intrusions to prove your security stack blocks real threats, not just theoretical ones.
Unencrypted local network traffic reveals sensitive data to anyone within physical or logical range of your wireless access points.
Static indicators of compromise often fail against modern adversaries because they only record what happened, not how the attacker achieved their goal.
Advanced persistent threats bypass perimeter defences by mimicking legitimate traffic and remaining dormant for months before exfiltrating data.
Standard browser protections now block most clickjacking attempts, but legacy interfaces and embedded frames remain vulnerable to user interface redress attacks.
Threat modeling shifts security from reactive patching to proactive architecture, exposing flaws in logic and data flow before code is written or deployed.
Web application firewalls filter traffic based on signatures, not intent, leaving logic flaws and authenticated attacks largely invisible to standard rule sets.
Most account takeover fraud detection fails because teams monitor login success rates while attackers rely on credential stuffing to bypass standard alarms.
Monitoring hidden networks shifts security from reactive incident response to proactive threat containment before data leaves your perimeter.
Trusting visual cues like SSID names is the primary failure point, as attackers replicate these identifiers with perfect fidelity to intercept unencrypted traffic.
Multi-region failover is a complex engineering discipline, not a simple backup switch, and treating it as such exposes your organisation to silent data loss and compliance breaches.
Removing write access for plugins reduces attack surface more effectively than installing additional security layers or scanning tools.
Open redirects bypass browser security checks by masquerading as trusted domains, allowing attackers to steal session tokens or facilitate phishing campaigns without hosting their own infrastructure.
Web cache poisoning allows attackers to serve malicious content to thousands of users by tricking servers into storing and re-serving tampered responses.
Proper network segmentation ensures that a compromised workstation cannot reach your financial servers, containing the breach within a single logical zone.
Broken access control is a broad category of failure, while IDOR is a specific object-level flaw that often hides inside larger permission gaps.