Unified Kill Chain: Small Business Defence Strategy
The Unified Kill Chain exposes the hidden gap between initial access and lateral movement, revealing where small teams waste resources on perimeter alerts.
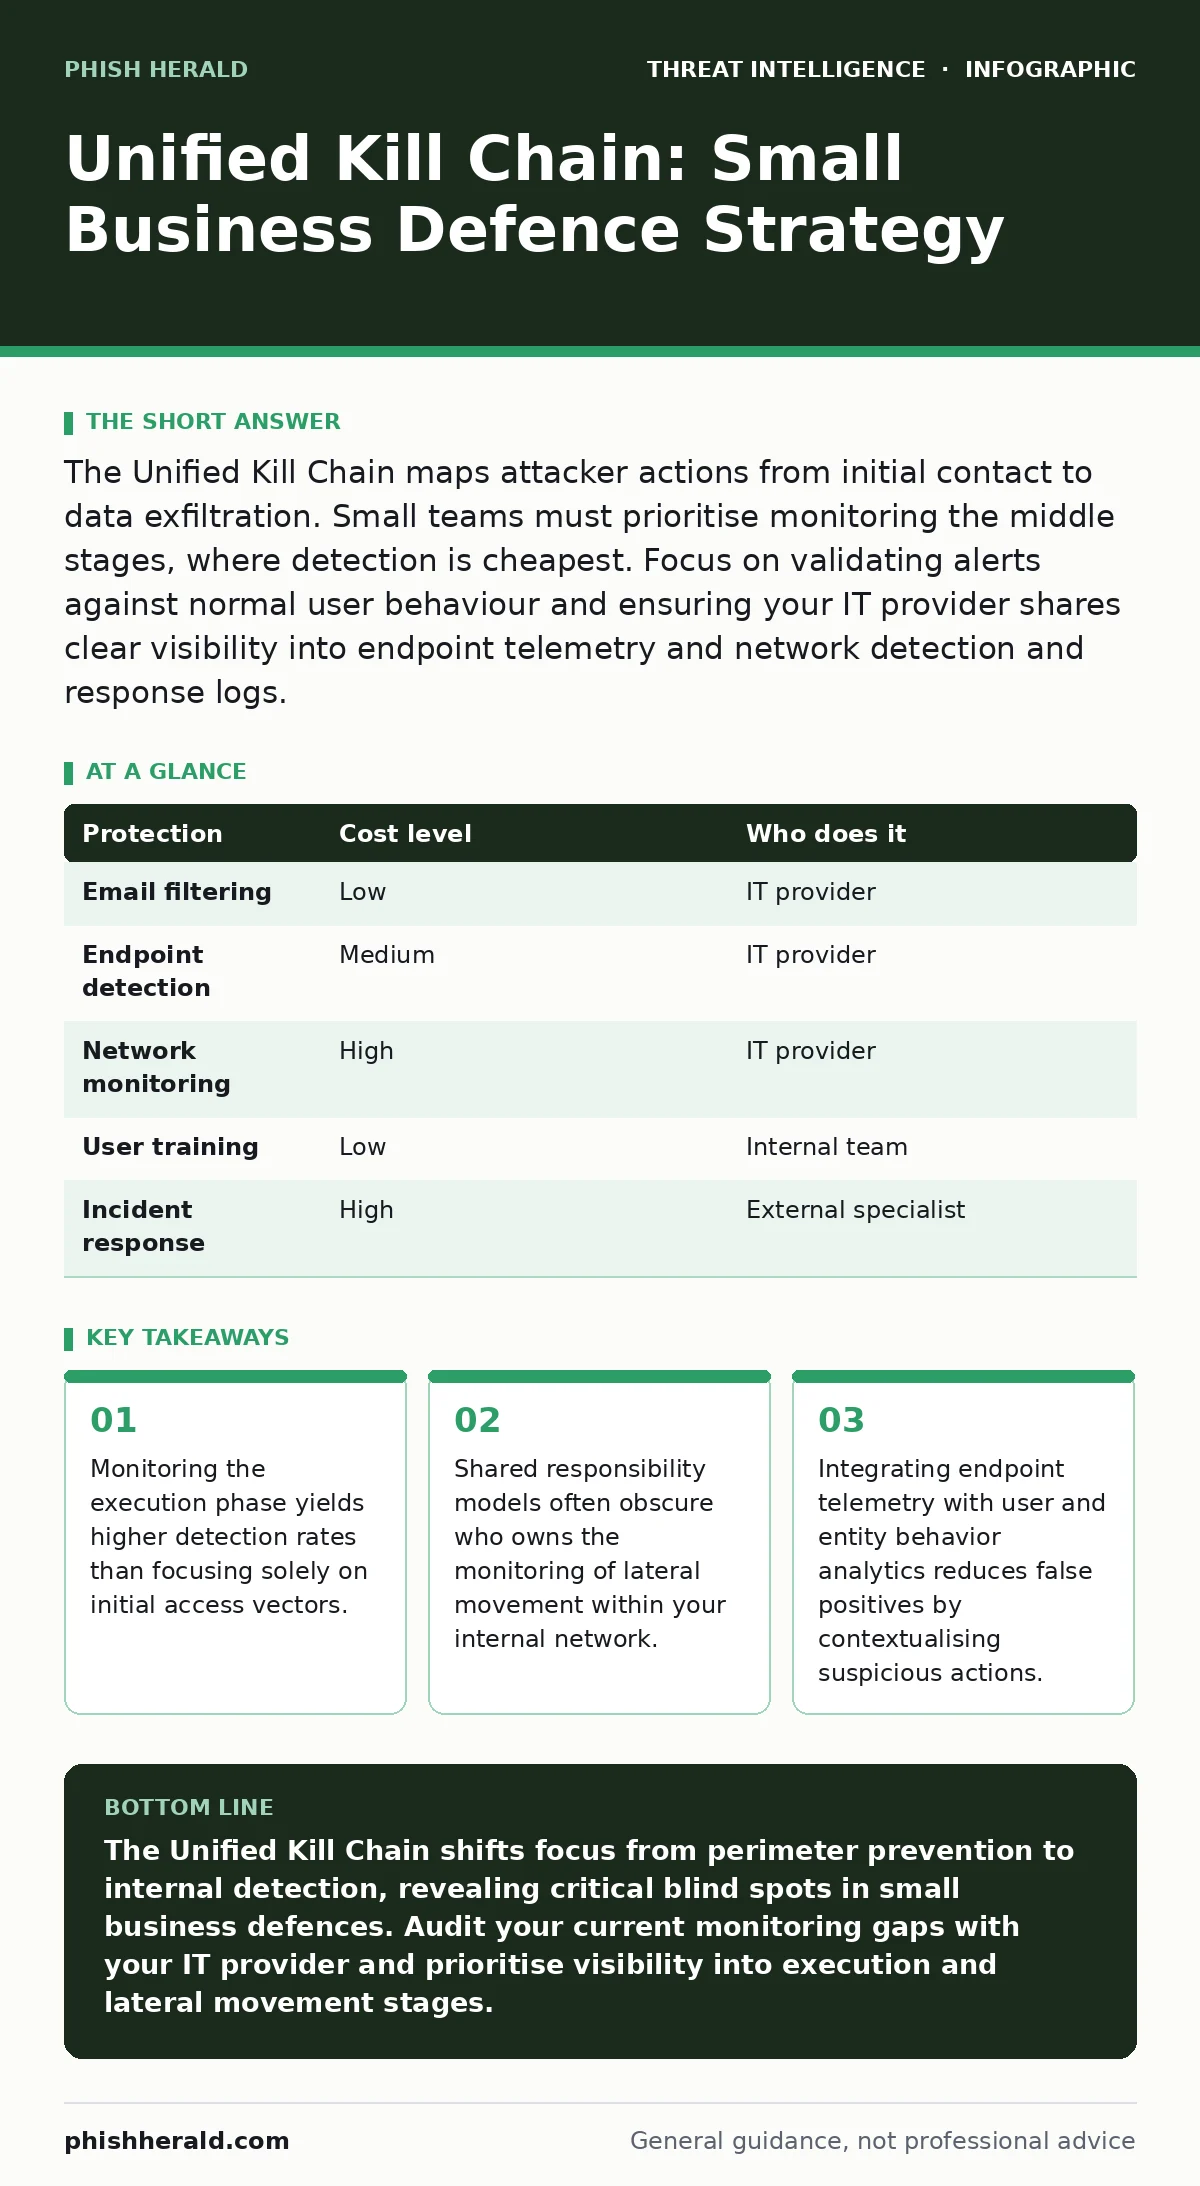
The Unified Kill Chain maps attacker actions from initial contact to data exfiltration. Small teams must prioritise monitoring the middle stages, where detection is cheapest. Focus on validating alerts against normal user behaviour and ensuring your IT provider shares clear visibility into endpoint telemetry and network detection and response logs.
The Unified Kill Chain Defined
The Unified Kill Chain is a framework that maps the lifecycle of a cyber attack from reconnaissance to objective completion. It extends traditional models by combining external attack paths with internal movement. You use this model to identify where your defences fail. Most small organisations focus heavily on the first stage, blocking emails and URLs. This creates a false sense of security. Attackers often bypass the perimeter using legitimate credentials or misconfigured cloud services. The framework forces you to consider what happens after the initial breach. It highlights the critical window between access and impact.
You must understand that no single tool covers every stage. Firewalls handle network traffic, but they miss fileless malware running in memory. Antivirus software detects known signatures, but it struggles with new variants. The Unified Kill Chain requires you to layer controls. Each layer adds visibility. This visibility allows you to catch attacks that slip through the first line of defence. You are not trying to stop every attempt. You are trying to detect the successful ones early enough to limit damage.
Why Scale Changes Strategy
Small teams lack the bandwidth for constant manual monitoring. You cannot watch every log entry. The Unified Kill Chain helps you prioritise. It shows which stages generate the most noise and which provide the clearest signals. At small scale, the cost of comprehensive monitoring is prohibitive. You must choose where to invest. The middle stages of the chain, such as execution and persistence, offer the best return on investment. These stages involve concrete actions on your devices. They leave traces that are easier to automate detection for than subtle reconnaissance.
Imagine a scenario where an attacker steals a password. This is an access issue. If you only monitor the login portal, you miss the subsequent data theft. The Unified Kill Chain pushes you to monitor the user's behaviour after login. This shift in focus is critical. It moves you from prevention to detection and response. Prevention fails eventually. Detection limits the blast radius. Small businesses survive attacks by limiting the damage, not by preventing every single entry attempt.
| Protection | Cost level | Who does it |
|---|---|---|
| Email filtering | Low | IT provider |
| Endpoint detection | Medium | IT provider |
| Network monitoring | High | IT provider |
| User training | Low | Internal team |
| Incident response | High | External specialist |
Practical Implementation Steps
You need to map your current tools to the kill chain stages. Identify gaps where you have no visibility. Start with execution. This is where malicious code runs. Ensure your endpoints send telemetry to a central system. Endpoint telemetry captures process creation, registry changes, and file modifications. Without this data, you are blind to what happens on your devices. Next, address persistence. Attackers install mechanisms to survive reboots. Detecting unusual scheduled tasks or startup items is vital.
Integrate your data sources. Siloed tools create blind spots. An alert on the endpoint might look normal in isolation. Combined with unusual network traffic, it becomes suspicious. Use user and entity behavior analytics to establish baselines for normal activity. When a user accesses files at 3 AM from an unusual location, the system flags it. This contextual data reduces alert fatigue. You focus on anomalies, not volume. Automation handles the routine checks. Your team investigates the exceptions.
Questions for Your IT Provider
Your IT provider manages your infrastructure. You must verify their approach to the kill chain. Do not accept vague promises of "security". Ask specific questions about visibility and response. Request a breakdown of their monitoring capabilities. You need to know if they detect lateral movement. Most small business providers focus on keeping devices online and patched. They often neglect internal network monitoring. This is a significant risk. Lateral movement allows attackers to reach critical servers after initial access.
Ask about their incident response plan. How quickly do they detect a compromise? Do they have playbooks for different attack stages? You need to know who is responsible for each stage. Some providers outsource monitoring to third parties. Ensure there is a clear chain of command during an incident. Ambiguity causes delays. Delays increase damage. Verify that they share logs with you. Transparency builds trust. It also allows you to audit their performance.
- Does your monitoring cover lateral movement within our internal network?
- How do you correlate endpoint telemetry with network detection and response data?
- What is your average time to detect a successful breach?
- Do you provide regular reports on detected and blocked attack attempts?
- How do you handle incidents that involve cloud services and hybrid environments?
The Cost of Blind Spots
Ignoring the middle stages of the kill chain is expensive. You pay for perimeter tools that miss the majority of sophisticated attacks. You also pay for incident response when the damage is already done. The cost of recovery far exceeds the cost of monitoring. Small businesses are particularly vulnerable because they lack redundancy. A single server compromise can halt operations. The Unified Kill Chain helps you avoid this outcome. It ensures you have eyes on the internal network.
Consider the hidden cost of alert fatigue. If your tools generate too many false positives, your team ignores them. Real threats get buried. Tuning your detection rules is essential. Use the kill chain to refine these rules. Focus on high-fidelity indicators. For example, a single failed login is normal. Five failed logins followed by a successful one and immediate data access is not. This contextual analysis improves accuracy. It saves time and resources.
See also: Input Validation for Small Teams: Secure Code Without the Budget · Dark Web Intelligence: Decisions, Risks and Team Usage
Integrating Advanced Concepts
You may encounter terms like advanced persistent threats or nation-state cyber attacks. These represent the high end of the threat spectrum. Small businesses are rarely the primary target of state actors. However, they are often used as stepping stones. Attackers compromise small networks to launch larger attacks. This makes you a target. Understanding tactics, techniques and procedures (TTPs) helps you defend against these opportunistic attacks. You do not need to defend against every possible threat. You need to defend against the ones that exploit your weaknesses.
Purple teaming can be adapted for small environments. It involves coordinated testing between offensive and defensive teams. You simulate attacks to test your detection capabilities. This reveals gaps in your kill chain coverage. It also trains your team to respond effectively. DCSync attacks are a specific technique where attackers replicate directory services to steal credentials. Monitoring for unusual replication events can detect this. It is a concrete example of applying kill chain principles. You monitor the action, not just the intent.
Continuous Improvement Cycle
Security is not a one-time project. It is a continuous cycle. You must regularly review your kill chain mapping. New tools emerge. New attack techniques develop. Your environment changes. Updates to your monitoring strategy are necessary. Schedule quarterly reviews with your IT provider. Assess new risks. Update your detection rules. Test your incident response plans. This discipline ensures your defences remain effective. It also keeps your team engaged and informed.
You must also educate your staff. They are the first line of defence. Phishing remains a primary entry point. Training helps them recognise suspicious activity. It reduces the success rate of initial access attempts. Combine training with technical controls. This layered approach provides the best protection. You cannot rely on people alone. You cannot rely on technology alone. You need both. The Unified Kill Chain provides the structure for this integration.
Key takeaways
- Monitoring the execution phase yields higher detection rates than focusing solely on initial access vectors.
- Shared responsibility models often obscure who owns the monitoring of lateral movement within your internal network.
- Integrating endpoint telemetry with user and entity behavior analytics reduces false positives by contextualising suspicious actions.
The Unified Kill Chain shifts focus from perimeter prevention to internal detection, revealing critical blind spots in small business defences. Audit your current monitoring gaps with your IT provider and prioritise visibility into execution and lateral movement stages.
Frequently asked questions
How does the Unified Kill Chain differ from the Lockheed Martin model?
The Unified Kill Chain combines external attack phases with internal lateral movement, providing a more complete view for organisations with limited internal monitoring capabilities.
Can small businesses implement endpoint telemetry effectively?
Yes, modern endpoint detection and response platforms automate data collection and analysis, making telemetry feasible for small teams without dedicated security analysts.
What is the biggest mistake small businesses make with this framework?
Focusing exclusively on blocking initial access while neglecting monitoring for post-compromise activities, which leaves them vulnerable to lateral movement and data theft.
How often should we review our kill chain mapping?
You should review your mapping quarterly to account for new tools, changes in your infrastructure, and emerging attack techniques that may bypass existing controls.
How this guide was produced: written by the Phish Herald editorial team with AI assistance, checked against the public references listed below, and reviewed when the facts change. See our editorial policy or report an error.