Stop Pass-the-Ticket Attacks: Practical Prevention and Detection
Kerberos tickets are often stored in memory rather than on disk, meaning traditional endpoint scanning frequently misses the primary attack vector for lateral movement.
Kerberos tickets are often stored in memory rather than on disk, meaning traditional endpoint scanning frequently misses the primary attack vector for lateral movement.
Rootkits hide by intercepting system calls, making standard security tools blind to their presence and allowing silent data exfiltration.

Unmanaged digital identities accumulate silently, creating hidden entry points that automated systems often fail to detect or revoke.

Defacement is often a noisy distraction that masks silent data theft, and the visual change is frequently the least damaging part of the compromise.

Most database activity monitoring fails because teams configure alerts for every query, creating noise that hides the actual theft of sensitive records.

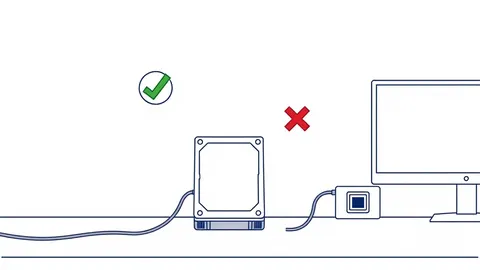
An offline backup is only secure if the storage medium remains physically disconnected from any network that could carry malware or ransomware.

A single directory path in a URL can bypass file storage controls and expose confidential data without requiring password authentication or complex exploits.

Potentially unwanted programs often evade detection by masquerading as legitimate utilities, leaving subtle behavioural traces rather than obvious signatures in system logs.

The most dangerous data in a leaked repository is often not the source code itself, but the transient secrets embedded in its history that survive deletion.

Cloud sync mirrors files in real time, meaning a ransomware infection or accidental deletion wipes the cloud copy instantly, whereas backup retains historical versions.

Attackers now steal data before encrypting systems, forcing victims to pay twice or face public leaks that damage reputation beyond financial loss.

Misconfigured lockout thresholds transform legitimate user errors into self-inflicted outages, creating a vulnerability window for attackers.

Merging cloud security tools reduces blind spots between code and runtime, turning fragmented alerts into a single, actionable view of risk.

Most container escapes occur not because of code flaws, but because the host kernel grants excessive privileges to a compromised process.

Modifying an object’s prototype allows attackers to inject properties that every instance inherits, bypassing standard checks silently.

Eliminate unnecessary remote access, enforce conditional access policies, and monitor session behaviour to neutralise the most common attack vectors targeting your network perimeter.

Prevent supply chain attacks by isolating build environments and verifying package hashes, blocking threats before they reach production servers.