Threat Intelligence
Dark web monitoring services: finding credential leaks before attacks happen
Automated surveillance of hidden forums reveals stolen credentials long before attackers deploy payloads against your network.
Everything Phish Herald has reported about threat intelligence: 7 stories, newest first. Part of our Threat Intelligence coverage.
Automated surveillance of hidden forums reveals stolen credentials long before attackers deploy payloads against your network.
Default installations leak your identity through exit relay sniffing, operational habits, and local OS artifacts rather than cryptographic flaws.
Tracking how attackers behave rather than what tools they use allows teams to detect threats that change their digital fingerprints daily.
Reconnaissance occurs silently on your internal networks long before any external perimeter breach, rendering traditional perimeter alerts useless against modern adversaries.
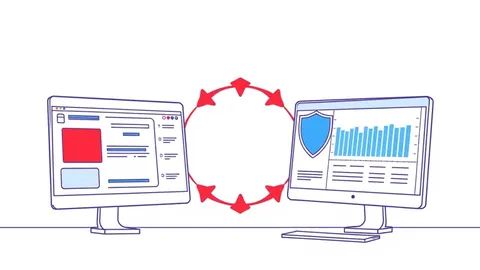
Purple teaming is not a single event but a continuous feedback loop that aligns attack simulation with detection engineering to close specific security gaps.
State-sponsored groups often mimic criminal gangs, use standard commercial tools, and target supply chains rather than launching direct, Hollywood-style assaults on your core infrastructure.
YARA rules provide high-fidelity detection by matching structural patterns in files and memory, but they require constant tuning to avoid performance degradation and alert fatigue.