Threat Intelligence
Tactics, Techniques and Procedures (TTPs) for Security Decisions
Tracking how attackers behave rather than what tools they use allows teams to detect threats that change their digital fingerprints daily.
Everything Phish Herald has reported about detection engineering: 4 stories, newest first. Part of our Threat Intelligence coverage.
Tracking how attackers behave rather than what tools they use allows teams to detect threats that change their digital fingerprints daily.
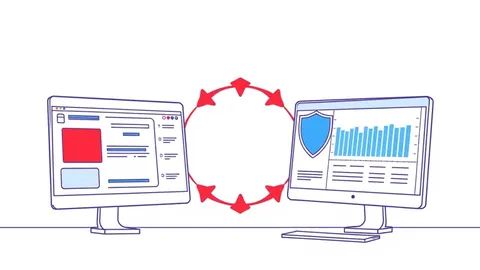
Purple teaming is not a single event but a continuous feedback loop that aligns attack simulation with detection engineering to close specific security gaps.
Endpoint telemetry transforms raw binary noise into structured intelligence, yet the collection phase often discards the context needed to prove intent.
Most organisations monitor only configuration files, leaving the executable code that attackers modify to bypass detection completely unwatched.